Cybersecurity · Ljubljana, Slovenia
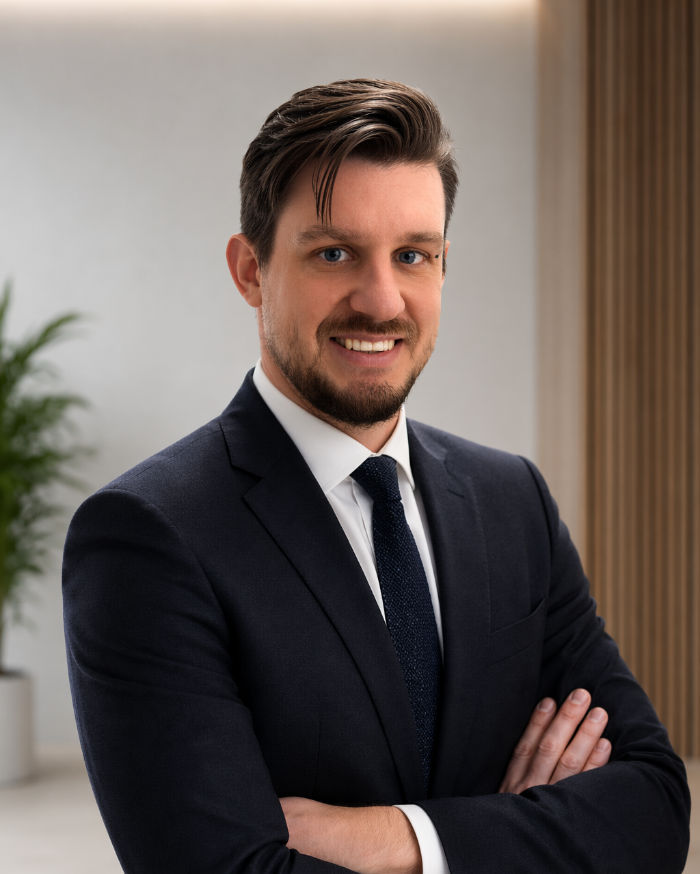
Erik Cvetek
Senior Cybersecurity Consultant
From threat detection & response to ISMS, ISO 27001, NIS2 and GRC - I defend business-critical assets and guide organizations to certification.
- $ whoami
- Erik Cvetek · Senior Cybersecurity Consultant
- $ cat focus.txt
- Cyber Defense · Security Operations · GRC
- $ ls ~/stack
- EDR XDR SIEM Email-Security
- $ cat governance.txt
- ISMS · ISO 27001 · TISAX · NIS2 · Internal Audit
- $ status
- ●▋
// about me
Defense in depth - from the SOC to the boardroom.
I'm a cybersecurity professional who works across the full spectrum of defense. On the technical side I manage and tune EDR / XDR, SIEM, and email and endpoint security, run threat detection and hunting, and lead incident response. On the strategic side I design and operate ISMS frameworks and prepare organizations for ISO 27001, TISAX and NIS2 certification - driving implementation and conducting internal audits.
That blend lets me connect day-to-day security operations with governance, risk and compliance - turning controls into measurable outcomes and aligning security with real business objectives. My focus stays the same end to end: minimize risk, strengthen resilience and enable secure innovation across the enterprise.
// what I do
Expertise
Hands-on technical defense and strategic governance - the full security lifecycle.
Cyber defense
-
Threat Detection & Response
EDR / XDR across endpoints and identities - detection engineering, proactive threat hunting and calm incident response with prepared playbooks.
-
Security Operations & SIEM
SOC monitoring, log correlation and alerting that surface real threats fast.
-
Email, Endpoint & Identity Security
Hardening the three primary attack vectors - anti-phishing, endpoint protection and identity security.
Governance & compliance
-
ISMS, ISO 27001 & TISAX
Implementation, certification support and internal auditing of ISO 27001 and TISAX - frameworks that actually stick.
-
NIS2 & GRC
NIS2 compliance, risk management and GRC programs that tie controls to real business outcomes.
-
Strategy & Architecture
Security roadmaps and secure-by-design architecture - from network and cloud to identity and Zero Trust - aligned with business strategy and risk appetite.
// career
Experience
A track record of building and leading security programs.
-
May 2025 – Present
Senior Cybersecurity Consultant
KP Consulting · Ljubljana, Slovenia
Guiding SME and enterprise clients to ISO 27001 and TISAX certification - from gap analysis and ISMS design to internal audits - and advising on NIS2 and GDPR compliance. Leading the cybersecurity team that defends client organizations: threat detection and response, incident handling and vulnerability management.
-
Oct 2022 – May 2025
Information Security Manager
Owned information security end to end - running the ISMS (risk assessment and treatment, internal audits, ISO 27001 and TISAX assessment preparation) and leading threat detection and response, vulnerability management, endpoint and email security and security awareness. Escalation point for security incidents, reporting posture and risk to IT management.
-
Jan 2019 – Sep 2022
IT Systems Security Specialist
Worked on ISO 27001 and TISAX implementation and internal audits, remediating findings across IT systems. As part of the global cybersecurity team, administered Microsoft Defender ATP, Azure ATP and Defender for Office 365, hardened Windows Server and Azure environments and ran vulnerability assessments.
-
Jul 2015 – Dec 2018
IT Systems Analyst
Joined the global cybersecurity team as central antivirus administrator - endpoint protection, malware handling and incident support. Root-level AD domain administrator; migrated servers and services to Microsoft Azure and administered Office 365 and core infrastructure (Hyper-V, ESXi, domain controllers).
-
Sep 2013 – Jul 2015
IT Support Technician
Administered local Active Directory, Windows and Unix servers, SQL databases and the network, supported ERP systems and built SSRS reports and .NET tools for the manufacturing environment.
-
Sep 2010 – Mar 2014
IT Support Technician & Sales
Sold mobile contracts while running local IT - device repairs, network and server administration, and web and desktop apps that simplified the field team's work. Where it all started.
// credentials
Certifications & education
Credentials and a working toolkit spanning cyber defense, governance and compliance.
Certifications
-
ISO/IEC 27001 Senior Lead Implementer
-
Certified SME Cyber Security Officer
-
Certified Ransomware Protection Officer
-
ITIL® Foundation Certificate in IT Service Management
Education
-
University of Ljubljana
Faculty of Computer and Information Science
Languages
- Slovene - Native
- English - C2 Proficient
Cyber Defense & Operations
- EDR / XDR
- SIEM / SOC
- Threat Detection & Response
- Threat Hunting
- Incident Response
- Vulnerability Management
- Security Architecture
- Security Awareness
Governance, Risk & Compliance
- ISMS
- ISO 27001
- NIS2
- GDPR
- TISAX
- VDA ISA
- Risk Management
- Internal Auditing
Security Platforms
- Microsoft Defender
- Microsoft Sentinel
- CrowdStrike
- SentinelOne
- Proofpoint
- Fortinet
- Microsoft 365
- Microsoft Entra ID
- Microsoft Purview
// get in touch
Let's secure what matters.
Need cybersecurity, information security, GRC or certification support for your organization? Reach out and I'll connect you with the right consulting engagement through KP Consulting.
connect@erikcvetek.com